Validating Research While Protecting Health Data
13 Oct 2026Independent validation can strengthen confidence in research findings. ADSI uses different validation approaches across analyses, depending on the data and research questions.
For analyses involving linked UW Health electronic health records and Wisconsin birth records, an additional challenge arises: how can an external team independently evaluate the analysis without direct access to protected health data?
How does it work?
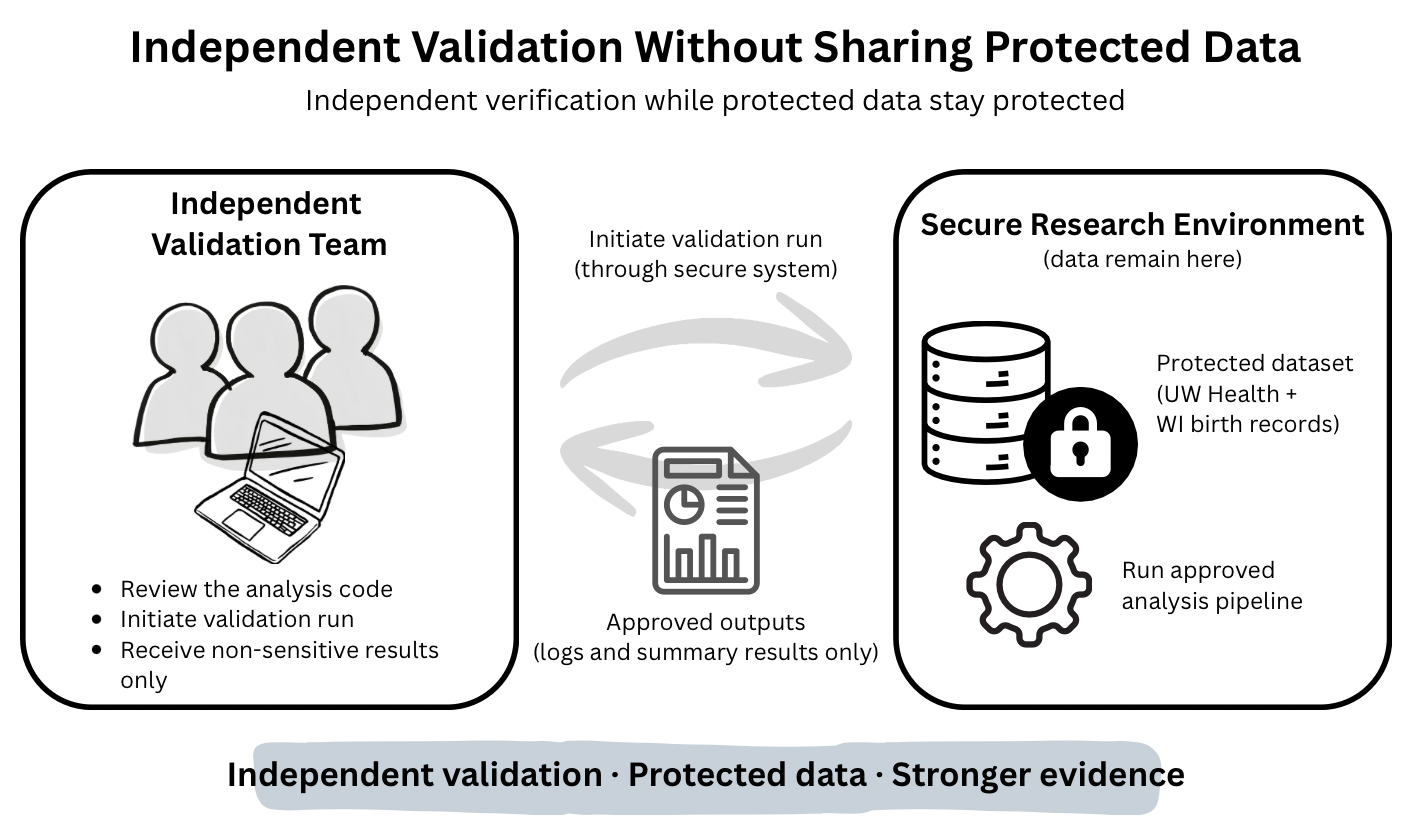
Our approach is designed around two separate secure computing environments.
The external validation team will be able to:
- Review the analysis code
- Initiate a validation run
- Review approved, non-sensitive results
The protected data:
- Remain in a separate secure environment
- Are accessible only to authorized researchers
- Are not directly accessible to the external validation team
Why separate the environments?
The separation allows independent researchers to evaluate whether the analytic workflow performs as intended without needing access to the protected linked health data themselves.
Together with synthetic-data testing and cybersecurity review, this approach is designed to balance: